Why 2f+1
blog
Have you ever wondered why byzantine agreement protocols seem to all start with the assumptions that less than a third of the participants can be malicious?
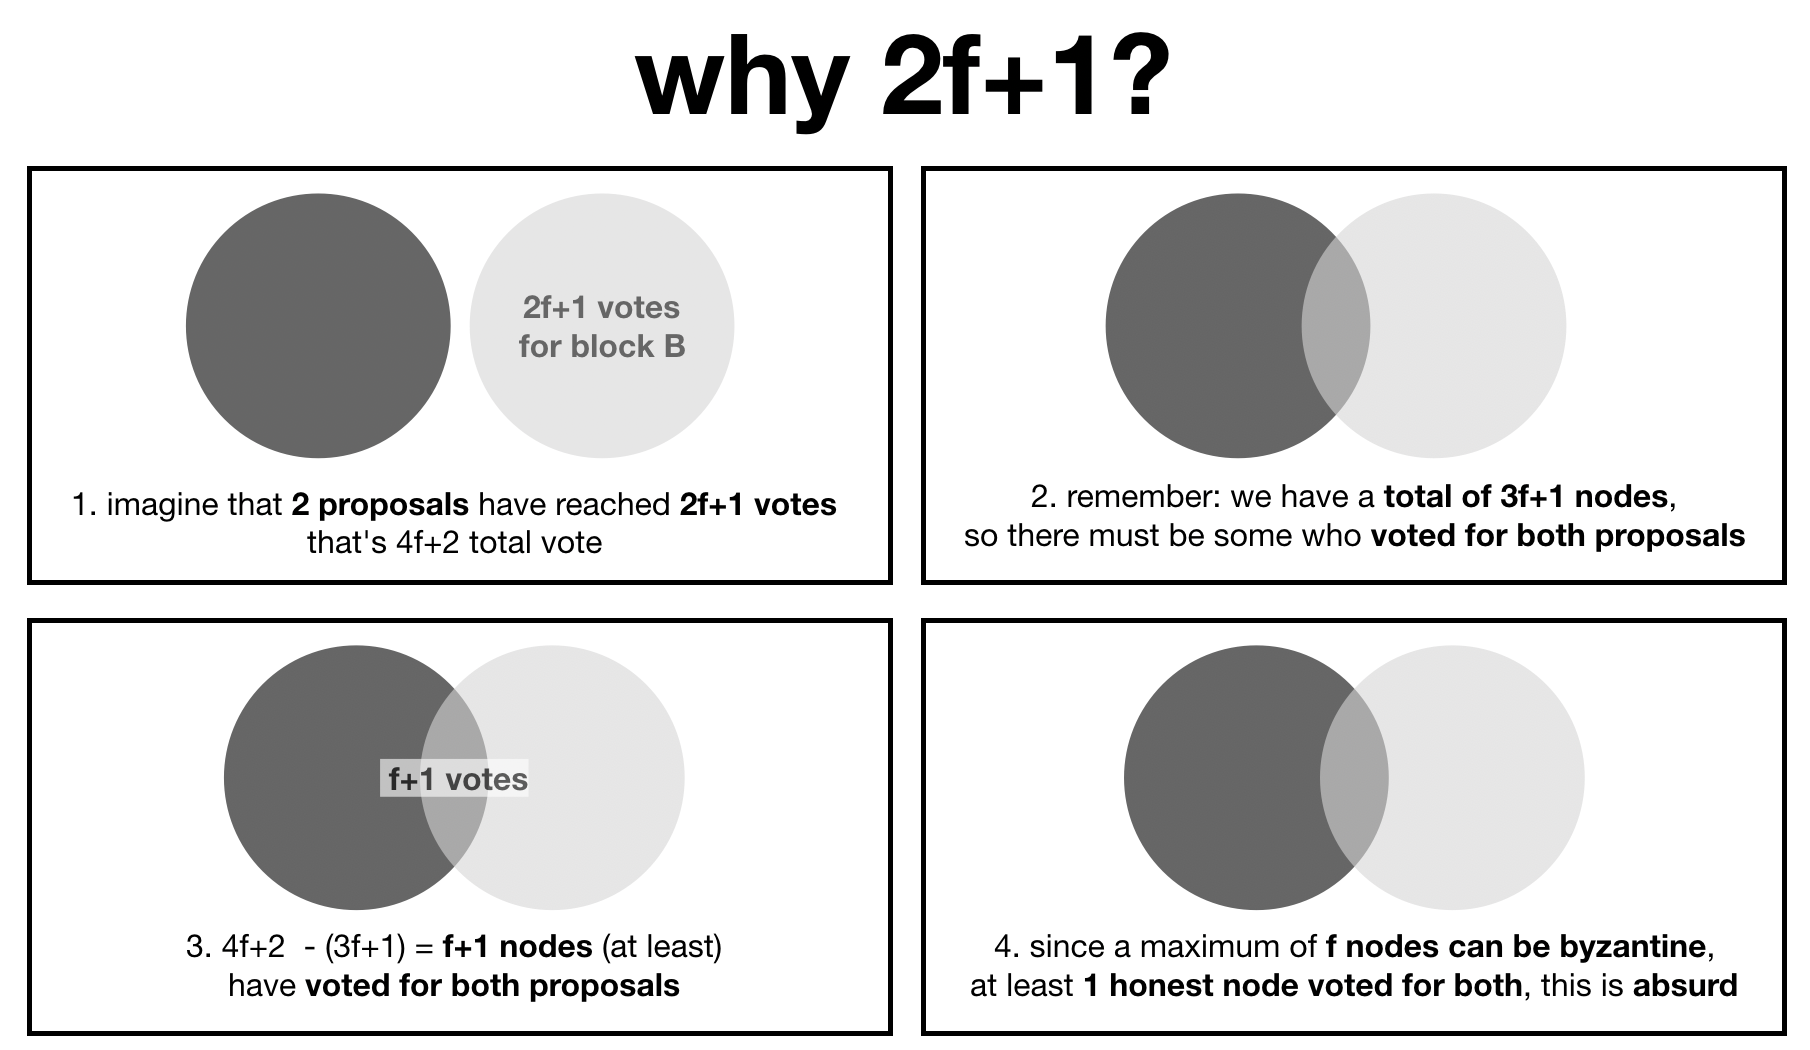
This axiom is useful down the line when you want to prove safety, or in other words that your protocol can’t fork. I made a diagram to show that, an instance of the protocol that forks (2 proposals have been committed with 2f+1 votes from the participants) is absurd.
suggested reads: